



Information Security for Your Business
- Certified Experts in ISMS and ISO 27001
- Customized Solutions for Every Industry
- Practical advice with lasting results
Trusted by 1000+ Customers


Information Security at intersoft consulting services
Information security touches on numerous areas simultaneously. An effective information security management system (ISMS) is essential today. We ensure its efficient implementation—from technical safeguards and regulatory compliance to organizational integration within the company.
intersoft consulting services covers all of these areas: Our information security consulting services range from ISMS implementation to certification preparation, internal audits, ISMS risk management and awareness campaigns, as well as consulting based on industry-specific standards. The overlap with our consulting areas of data protection and IT forensics enables a holistic consulting approach.
See for yourself the benefits of working with us.
- Certified Information Security Professionals
- A wealth of experience
- Custom Solutions
Our Services for Your Information Security
We support you in all aspects of information security—from the initial assessment to successful certification.
ISMS and Certification
We’ll guide you through the structured implementation of your ISMS and help you prepare specifically for certification.
NIS-2
We provide comprehensive support to help you achieve NIS 2 compliance.
External ISB and CISO
Our certified experts take on the role of Information Security Officer or CISO and integrate seamlessly into your organization.
More
From analysis to knowledge transfer to expert consulting—we support you at every level of information security.
Who is information security relevant to?
Information security is not limited to specific industries or company sizes. As soon as business-critical information is processed—whether customer data, contracts, development documents, or financial data—systematic protection is essential. Regulations such as NIS-2 and DORA require companies to implement verifiable security measures, and an increasing number of business partners now require a certified ISMS in accordance with ISO 27001 or TISAX.
intersoft consulting services helps you identify the requirements relevant to your business and establish an ISMS that not only meets regulatory requirements but also strengthens the trust of your business partners. We offer all of this in a practical manner, regardless of your industry.
Our expertise protects your data – intersoft consulting services
As an experienced specialist, intersoft consulting services has been combining information security and data protection for over two decades. This synergy makes our consulting services particularly effective—because security concepts are only effective when they also take regulatory and organizational requirements into account.
- Information Security and Data Protection from a Single Source
- All common standards and industries covered
- Verifiable Results Through Independent Certification
- Field-tested document templates included
Our Locations Near You
Personalized advice is important to us. We are here for you throughout Germany and are always available to assist you.
What Sets Us Apart
Ralf Lüneburg
Information Security Consultant
I’d be happy to advise you
Give us a call or send us a message using the contact form.
Information Security According to Industry Requirements
Every industry has its own regulatory requirements. We understand the specifics and provide you with tailored advice:
What is an Information Security Management System (ISMS)?
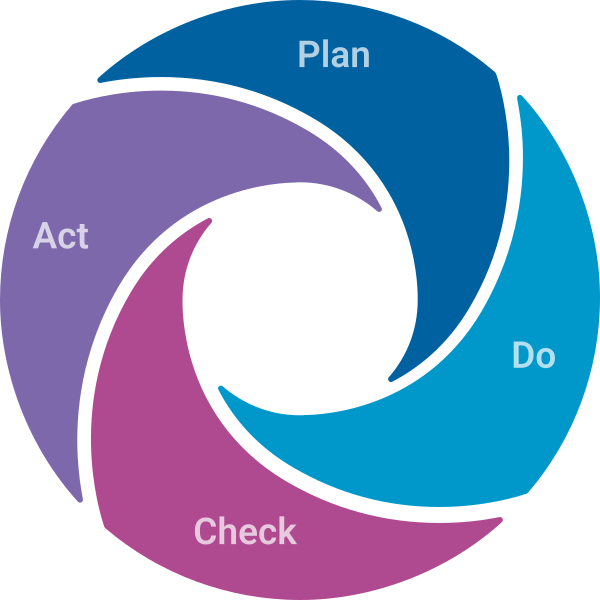
An Information Security Management System (ISMS) serves as the organizational backbone for the systematic protection of information. It defines policies, processes, and responsibilities for identifying, assessing, and appropriately addressing risks. ISO 27001 provides the internationally recognized framework for this. For many companies, this has long been a prerequisite for business relationships.
Your Path to ISMS with intersoft consulting services:
- Assessment and Risk Analysis
- Selecting the appropriate standard (ISO 27001, IT‑Grundschutz, TISAX, etc.)
- Structured ISMS Implementation Through Certification
- Continuous Improvement and Operations
What Our Customers Say
Testimonials from people who have already gotten to know and appreciate us.
The Information Security Process
Our structured consulting approach guides you through five sequential workshops, from the initial orientation to a fully functional risk management system.
ISMS Intensive Training
To begin with, we ensure that all project participants have a solid understanding of the chosen standard—whether it’s ISO 27001, IT‑Grundschutz, or an industry-specific set of guidelines. In doing so, we work together to clarify which requirements are relevant to your company and what key terms such as “scope” or “interested parties” actually mean.

GAP Analysis and Planning
In the second step, we assess the current state of your information security and identify existing gaps relative to regulatory requirements. Based on this, we develop a concrete action plan with clearly defined work packages and responsibilities.

Structure of the ISMS Documentation
You’ll receive our tried-and-true template package containing all the documents required by ISO 27001. Since 70 to 80% of the content is already pre-structured, you can jump right into editing the content. Our experts will explain the structure and use of each template.
Structure of the ISMS Core Processes
We will then establish the core control processes of your ISMS and integrate them with your existing documentation. This includes all recurring tasks, such as audit planning, the continuous improvement process, and management reporting.
Establishing an Appropriate ISMS Risk Management Framework
Finally, we will work with you to develop a risk management system that builds on your existing processes. This involves identifying corporate assets, analyzing hazards, and assessing and addressing risks according to defined criteria.
Ralf Lüneburg
Information Security Consultant
I’d be happy to advise you
Give us a call or send us a message using the contact form.
Your Information Security Consultants at intersoft consulting services
Certified expertise with a personalized approach—right here for you
Information security requires a broad range of expertise. Our team includes BSI-certified ISO 27001 audit team leaders based on IT‑Grundschutz, ISO 27001 lead auditors and implementers, and TÜV-certified IT security officers. This expertise is complemented by DORA ICT risk managers, business continuity managers, and specialists in cloud information security in accordance with ISO 27017/27018.
For you, this means: Whether you’re dealing with the strategic direction of your ISMS, technical vulnerability analyses, or preparing for a certification audit—at intersoft consulting services, you’ll find the right expertise. Your personal contact person coordinates the collaboration and has a detailed understanding of your situation.
Thanks to their independence and neutrality, our external consultants can objectively evaluate all security-related aspects without being influenced by internal conflicts of interest.
Practical experience is a key factor for success in consulting. Over the years, we have gained both theoretical knowledge and practical experience across a wide range of industries and company sizes. Thanks to this practical experience, we are able to identify solutions that are both legally compliant and practical.

Recognized Through Certificates & Memberships
After years of work in the field of information security, we have earned a wide range of Certificates and memberships.


Ralf Lüneburg
Information Security Consultant
Free Initial Consultation
We’re happy to answer your questions. Please feel free to contact us using our contact form.

Dr. A. Preuß, Managing Director
cut-e
V. Ring, IT Department
Westdeutsche Spielbanken
Erwin Mees, ISMS Project Manager and IT Security Officer
KEW Kommunale Energie- und Wasserversorgungs AG
D. Halfmann, Deputy Human Resources Manager
Dohle Handelsgruppe