


External Data Protection Officer: Your Personal Expert
- More than 60 lawyers with specialized expertise
- A practical and solution-oriented consulting approach
- Personalized, with quick response times
Trusted by 1000+ Customers


What is an external data protection officer at Intersoft Consulting Services?
An external data protection officer (eDPO) is a specialized expert who is engaged as a service provider to assist companies in complying with data protection obligations. Unlike internal employees, the eDPO acts as an outsider. The basis for the collaboration is a service agreement that clearly defines the services and costs.
The independence of the external data protection officer is a key factor. He reports directly to senior management but maintains a neutral position free from instructions. Thanks to this independence, assessments can be made without conflicts of interest and thus objectively.
Companies are free to choose whether to appoint an internal or external data protection officer. This is governed by Article 37(6) of the GDPR.
When is an external data protection officer required?
Even companies that are not legally required to appoint a data protection officer can benefit from an external data protection officer. For example, when they are seeking external advice on data protection and want to avoid the high hourly rates charged by law firms, or when they want experts to handle obligations such as training their own employees. Our external data protection officers work proactively to ensure that legal requirements are implemented efficiently and in a practical manner.
Under the GDPR and the BDSG, there is a legal obligation to appoint a data protection officer in the following cases:

At least 20 people
A company employs at least 20 people who process personal data on a continuous and automated basis (Section 38 of the Federal Data Protection Act (BDSG); rule of thumb: 20 or more employees with a computer or user account).

Personal Data
A company’s core business involves the extensive processing of specific types of personal data, such as health data, biometric information, or information regarding criminal offenses.

Data Protection Impact Assessment
Data processing operations that pose a high risk to the rights and freedoms of data subjects are carried out, which necessitates a data protection impact assessment.

Market Research or Opinion Polls
Personal data is processed for the purposes of market research or opinion polling.

Video Surveillance
Video surveillance is in place, during which personal data is collected on a large scale.
intersoft consulting compared to other providers of external data protection officers
Software-focused
Typical providers of external DSB services
- Self-Service via Software
Digital tools and templates for self-service—personal consultation available only as a paid add-on. - Constantly changing points of contact; only remote
inquiries end up in the ticket system. No dedicated advisor, no industry knowledge, no personal contact. - Reactive rather than proactive
Only takes action in response to a specific request—no initiative or proactive advice. - Data protection only, no big-picture view
Isolated data protection consulting with no connection to IT security or technical audits. - Compliance Only on Paper
Automated templates suggest security, but rarely stand up to scrutiny.
Consulting with a Personal Touch
intersoft consulting as an external DPO
- Dedicated legal contacts instead of anonymous tickets
Personal contacts specializing in data protection law. - Your contact person can also be on site if desired.
Upon request, our consultants will come to you – throughout Germany, in person and not just via video call. - Proactive and forward-looking
Regular meetings and active support for your data protection organization—not just when requested. - Data Protection, Information Security & IT Forensics
Interdisciplinary teams with legal, technical, and IT forensic expertise. - True compliance, not just paperwork
Risk-based implementation—supported by our Guardileo software.
We’re not a software!
We are lawyers, information security experts, and consultants who provide you with personalized and proactive data protection support.
Dr. Alina Weskamp-Nordmann, LL.M.
Lawyer
I’d be happy to advise you
Give us a call or send us a message using the contact form.
What responsibilities do we handle as an external data protection officer?
Pursuant to Article 39 of the GDPR, the main responsibilities of an external data protection officer are: to provide information and advice to the controller and employees, to monitor compliance with data protection regulations, to provide advice on data protection impact assessments, and to cooperate with supervisory authorities.
Our team of highly qualified attorneys, who specialize in the GDPR, the Federal Data Protection Act, and the Telecommunications and Digital Services Data Protection Act (TDDDG), as well as other aspects of IT law, is available to advise you around the clock. In their role as external data protection officers, they handle all your data protection needs and relieve you of all legally required tasks.
A dedicated contact person will be available to support you both strategically and with day-to-day operational implementation.
A systematic approach that takes into account the various areas of the organization is necessary to fulfill data protection obligations. As external data protection officers, we view data protection as an integrated system in which all components build on one another and reinforce each other.

“Take advantage of our comprehensive knowledge of the GDPR, the Federal Data Protection Act, and the Telecommunications and Digital Services Data Protection Act. We are your dedicated point of contact and will help you implement all data protection requirements both strategically and operationally.”
Dr. Nils Christian Haag, Member of the Executive Board
Liability & Penalties: How and from what does an external data protection officer protect you?
Companies can suffer significant damage as a result of data breaches. An external data protection officer is a strategic partner who implements multi-layered safeguards, thereby strengthening the trust of employees, customers, and business partners.
Lower risk of fines and penalties
An external DPO brings specialized expertise regarding the complex General Data Protection Regulation (GDPR), which helps proactively prevent violations. Through regular audits and the implementation of key processes, the likelihood of substantial fines from supervisory authorities is significantly reduced.
Up-to-date Legal Knowledge and Training
A professional external data protection officer keeps his or her knowledge of the latest legislative changes and court rulings up to date—something that is often difficult for non-experts. This expert knowledge ensures that all measures comply with current requirements, which serves as a strong defense against allegations of organizational negligence in the event of a liability claim.
Mitigation of Direct Liability of Managing Directors
When fines are imposed under the GDPR, managing directors may also face personal liability within the company. Appointing a qualified external DPO can significantly minimize this risk in the event of a claim. intersoft consulting has one of the highest limits of liability insurance coverage on the market.
Reversal of the Burden of Proof in the Event of Damage
Appointing an external DPO and following his or her recommendations serve as important evidence of the company’s due diligence. In the event of a data breach or a regulatory audit, this can play a significant role in helping a company refute allegations of organizational negligence and thereby avoid fines and claims for damages.
Independent and Objective Advice
An external DPO operates completely independently of the company’s internal structures and can therefore objectively assess data protection compliance and make recommendations. This objectivity is crucial for identifying vulnerabilities early on and effectively minimizing the company’s liability risks.
Reduced Organizational Burden Through Clear Responsibilities
An external DPO ensures clearly defined processes, responsibilities, and documentation requirements for data protection. This structural clarity reduces the risk of internal errors and serves as evidence—in the event of an audit or liability claim—that the company has properly fulfilled its organizational obligations.
“We provide you with one-time coverage through our financial loss liability insurance of €20 million, and we haven’t had a single claim so far!”
Thorsten Logemann, Chairman of the Management Board
What are the costs of hiring an external data protection officer?
Starter
For small businesses with minimal consulting needs and up to 100 employees
starting at 360 €
+ One-time data protection audit starting at €1,500
- eDSB Certificate of Appointment
- Proactive legal advice from fully qualified attorneys
- dedicated personal contacts
- Response time: up to 72 hours (on business days)
- Quarterly Meeting
- Handling Data Subject Requests and Data Breaches
Additional Services
- Guardileo Trainer
E-Learning Courses - Guardileo Manager
Data Protection Management System
Most Popular
Business
For medium-sized companies with regular consulting needs and up to 500 employees
starting at 720 €
+ One-time data protection audit starting at €2,900
- Includes all services from the Starter package
- Response time: up to 48 hours (on business days)
- monthly regular meeting
- Establishing a Data Protection Management System
Additional Services
- Guardileo Trainer
E-Learning Courses - Guardileo Manager
Data Protection Management System
Premium
For large companies with significant consulting needs and 500 or more employees
upon request
+ One-time privacy check
- Includes all features from the Business plan
- Response time: up to 24 hours (on business days)
- Flexible regular meetings as needed
- Interdisciplinary consulting in the field of information security and IT forensics
- 24/7 emergency hotline, if needed
including
- Guardileo Trainer
E-Learning Courses - Guardileo Manager
Data Protection Management System
Here’s how our prices are calculated
While investing in an external data protection officer may initially seem like an additional expense, upon closer examination it often proves to be a sound business decision.
In addition to salary costs, in-house data protection officers also incur ongoing expenses for training and professional development. Furthermore, valuable work time is lost that the employee could otherwise devote to their actual duties.
External data protection officers do not have special protection against termination and are contractually liable for their work, which often tips the cost analysis in favor of the external solution.
- Company size and number of employees
- Industry and Category of the Processed Data
- Scope of Data Processing Activities
- Organizational Structure and Number of Branches
- IT Infrastructure
- Current Status of Data Protection Measures
Instead of relying on standard solutions, we take into account the specific processes and structures involved in your handling of personal data. Thanks to our extensive experience, we are able to develop a customized data protection solution that best meets your needs.
Our Data Protection Consultants
Certified expertise with a personalized approach—right here for you
The quality of data protection consulting is determined by professional qualifications and practical experience. Trust is the foundation of data protection, which makes a personal and individualized collaboration essential. The decision to hire an external data protection officer should therefore be based on solid qualifications and proven expertise.
We have a team of experienced legal professionals who specialize in the GDPR, the Federal Data Protection Act, and the Telecommunications and Digital Services Data Protection Act (TDDDG). Our consultants are also qualified through DEKRA- and TÜV-certified training programs.
We view ongoing professional development as a fundamental obligation. Our consultants regularly participate in training courses and seminars, as data protection law is constantly evolving. These training programs cover both legal updates and the latest technical developments.
With your external data protection officer, you’ll have a dedicated point of contact who understands your company’s structure and addresses your specific needs. This approach builds trust and ensures compliance with legal requirements when dealing with customers, regulatory authorities, and data subjects. Our consultants communicate clearly and comprehensibly.
Thanks to their independence and neutrality, our external data protection officers can objectively assess all aspects of data protection law without being influenced by internal conflicts of interest.
Practical experience is a key factor for success in data protection consulting. Over the years, we have gained both theoretical knowledge and practical experience across a wide range of industries and company sizes. Thanks to this practical experience, we are able to develop solutions that are legally compliant, workable, and pragmatic.
On-site throughout Germany
Dr. Alina Weskamp-Nordmann, LL.M.
Lawyer
Free Initial Consultation
We’re happy to answer your questions. Please feel free to contact us using our contact form.
Recognized Through Certificates & Memberships
After years of work in the field of data protection, we have earned a wide range of Certificates and memberships.


Your Benefits at intersoft consulting
The decision to hire an external data protection officer offers clear benefits for your company. Thanks to our experience, we can effectively strengthen your data protection framework while conserving your resources.



Our Process for Appointing a Data Protection Officer in a Few Steps
A structured approach is crucial for quickly and efficiently establishing an external data protection officer in your company. Our consulting process is deliberately structured in a clear and straightforward manner so that you can quickly benefit from our expertise
Your inquiry
After receiving your inquiry, we will contact you as soon as possible. Together, we will analyze your specific needs for an external data protection officer, taking your individual requirements into account. You can contact us by email at any time, even outside of regular business hours. Of course, you can also reach us by phone or schedule an appointment directly.
The Offer
We will then promptly prepare a customized proposal for you based on the needs assessment. We would be happy to invite you to an introductory meeting, during which we will introduce you to our company and your future data protection officer. The purpose of this meeting is to finalize the proposal and address any outstanding questions regarding our collaboration.
Conclusion of a Contract
Once everything has been finalized, you will receive a draft contract tailored to your needs. The service agreement outlines the terms of the collaboration between your company and us as an external service provider.
After the contract is signed, we will, upon request, register your external data protection officer with the relevant supervisory authority.
Privacy Check
We begin our collaboration with a data protection audit at your company. During this audit, we conduct an on-site assessment of all data protection-related processes and systems in accordance with the GDPR, check them for potential vulnerabilities, and evaluate them in terms of their risk potential. To address any identified deficiencies, the data protection officer develops practical recommendations for action. All results of the assessment are then summarized for you in a detailed report and listed according to risk.
Ongoing Data Protection Support
As part of our ongoing data protection support, we assist you—as your external data protection officer—in implementing the measures recommended in the data protection assessment, taking care not to place an unnecessary burden on your business processes and prioritizing actions based on risk. In addition, we are available to advise you and your employees on all questions related to data protection under the EU GDPR, helping to develop practical solutions that take into account both legal requirements and your business objectives and corporate culture.
Dr. Alina Weskamp-Nordmann, LL.M.
Lawyer
I’d be happy to advise you
Give us a call or send us a message using the contact form.
Data Protection Consulting by intersoft consulting
See for yourself the benefits of working with us.
- Certified IT Professionals
- A wealth of experience
- Custom Solutions
Data Protection Software as an Integral Part of Our Support Services
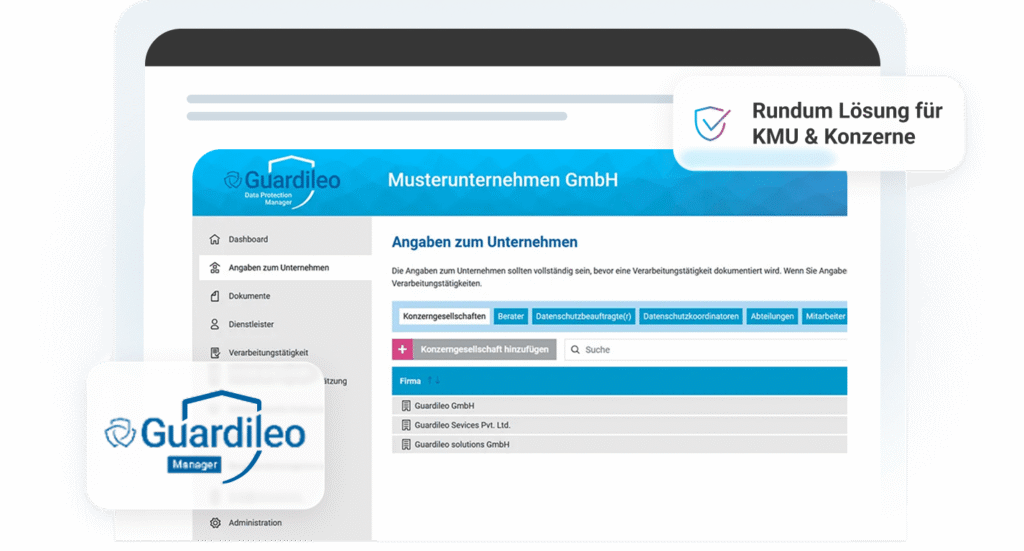
We rely on modern tools to efficiently comply with legal requirements. Our data protection software is a key component of our support model; it assists us in our role as external data protection officers and supports your internal processes.
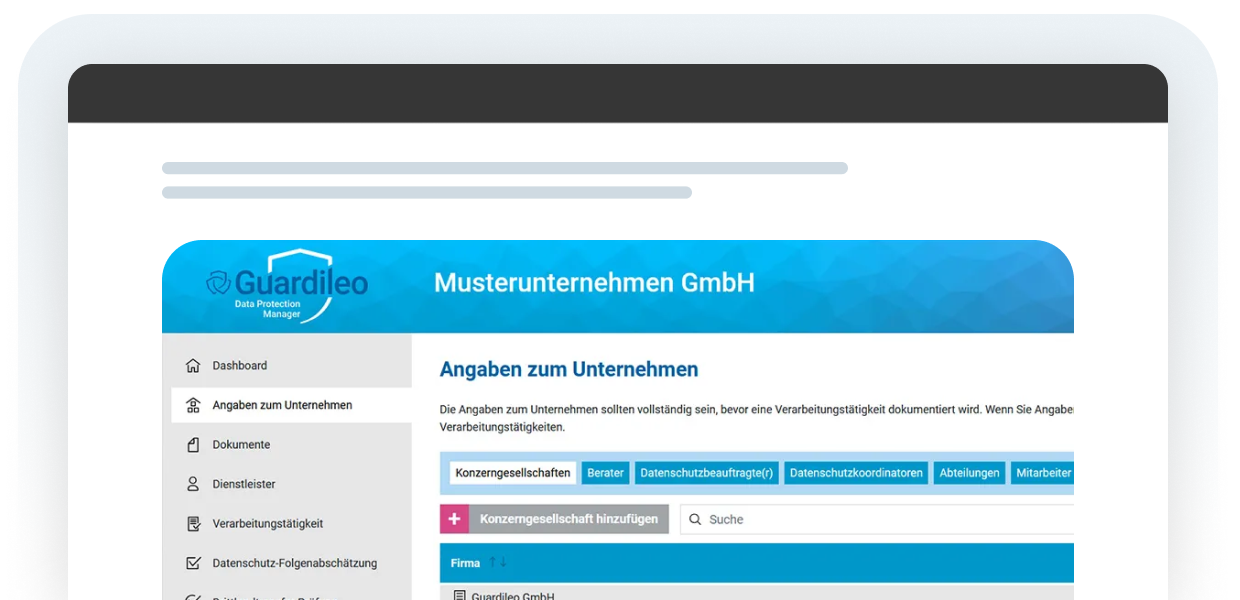
Our data protection software, Guardileo, supports our personalized consulting services in establishing structured processes to ensure compliance with the GDPR. It serves as the central platform for data protection management, risk management, documentation, and training.


Our expertise across all industries
Data protection challenges vary significantly depending on the industry. An external data protection officer must understand the industry-specific nuances and be able to develop appropriate solutions.
Different industries each have their own requirements and regulations. The necessary data protection measures vary greatly depending on the organization, because companies in different industries often have very different organizational structures. Experience in the specific field is a key criterion for selecting an external data protection officer.
In our role as external data protection officers, we support companies in a variety of fields. Thanks to our extensive industry knowledge, we are able to work across various sectors. We develop data protection strategies for different sectors, which are continuously optimized.
We are here to support you with highly qualified attorneys who specialize in the GDPR, the Federal Data Protection Act, the Telecommunications and Digital Services Data Protection Act (TDDDG), and other areas of IT law. A dedicated contact person who understands your industry will provide you with both strategic and operational advice.

Dr. Alina Weskamp-Nordmann, LL.M.
Lawyer
Free Initial Consultation
We’re happy to answer your questions. Please feel free to contact us using our contact form.
In-house or external data protection officer?
Existing professional qualifications
: Time-consuming and costly training is required to obtain professional qualifications.
No protection against dismissal
Special protection against dismissal for internal data protection officers, comparable to that of works councils.
Transparent Costs
Our cost estimates provide you with clear transparency and planning certainty.
An Unbiased Approach
With an in-house data protection officer, there is a risk of becoming blind to one’s own practices.
Knowledge of business processes
The external data protection officer must first familiarize himself with business processes.
Freeing Up Internal Resources
Our staff resources keep the internal time required to a minimum.
No right of co-determination for the works council
The right of co-determination of the works council (§ 99 BetrVG) does not apply to the external data protection officer.
Experience from other companies
Experience from other companies provides opportunities for comparison and practical solutions.
Independent Data Protection
The internal data protection officer is viewed by third parties as biased.
Neutral Position
Neutral Position helps, for example, by mediating between companies, works councils, and employees.
